Analysis
8 MIN READ
TL;DR
A heavily obfuscated zsh script performs light hardware fingerprinting as camouflage, then decrypts an embedded AES-128-CTR + gzip payload. The decrypted second stage:
Beacons to a C2/telemetry endpoint (
atlas-compass.com)Downloads a binary from
quest-22.comClears quarantine attributes (
xattr -c)Executes the binary from
/tmp/helper
The downloaded binary is a Universal (x86_64 + arm64) Mach-O packed loader. It contains a small cleartext stub that uses dlsym for dynamic API resolution and a large high-entropy encrypted section. At runtime the stub decrypts the real payload.
VirusTotal confirms the family as AMOS (Atomic macOS Stealer) / Camelot (trojan.amos/camelot).[1]
The domain quest-22.com has been linked to recent malvertising campaigns distributing macOS infostealers via fake Homebrew installers. The current campaign uses a Google Sites landing page (sites.google.com/view/brewapp) that closely clones the official Homebrew install page and is promoted via Google Ads.[2][3][4]
Sandbox observations (VirusTotal): The sample (executed as ./update) exhibits additional stealth, C2, and defence-impairment techniques, contacts Apple CDNs and related infrastructure, performs extensive filesystem probing, and shows behavioural similarity to known MacOS Mirage / Zenbox samples.
Distribution / Infection Vector
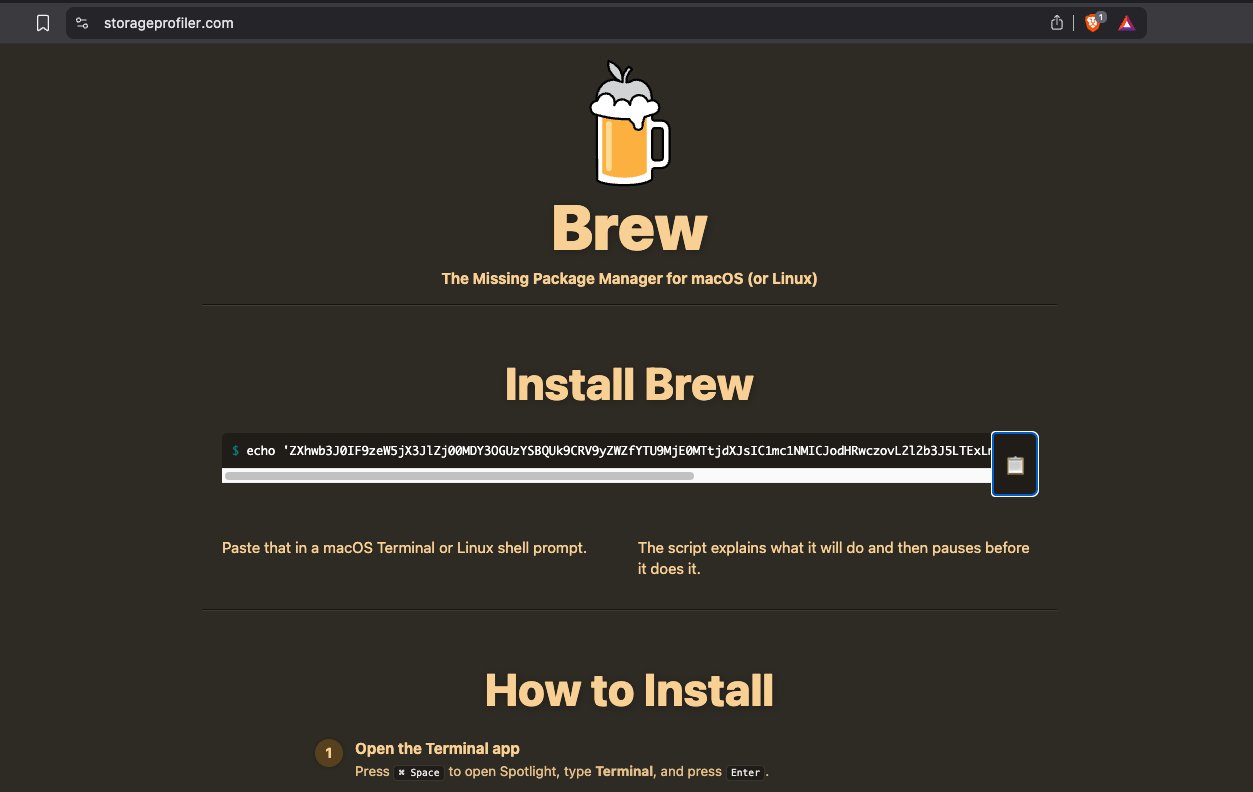
The sample is distributed via a malvertising campaign that impersonates the official Homebrew package manager.
Landing Page
URL:
https://sites.google.com/view/brewappHosted on Google Sites (free Google hosting)
A visual replication of the legitimate Homebrew install page:
Dark background
Official-looking logo
Same layout, typography, and step-by-step instructions
Title: “Brew – The Missing Package Manager for macOS (or Linux)”
How the victim is infected
User searches Google for “install homebrew”, “homebrew mac”, etc.
A Google Ad appears at the top of the results. The ad often displays the legitimate domain
brew.shin the preview.Clicking the ad redirects the user to the Google Sites page (
sites.google.com/view/brewapp).The page shows a code block containing an install command and instructs the user to:
Open the Terminal app
Copy the command
Paste it into Terminal and press Enter
The command presented is the heavily obfuscated Layer 1 zsh script analysed in this report.
Once executed, the script decrypts and runs the second-stage payload, which downloads and executes the AMOS/Camelot packed loader.
This is a classic ClickFix / social-engineering technique: the victim themselves pastes and runs the malicious command under the belief they are installing legitimate software.[3][5]
The same campaign has been observed using multiple Google Sites pages and rotating domains over time (e.g. earlier variants used brewe.sh, homabrews.org, etc.).[2][4][6]
Layer 1 – Outer Script Analysis
Decoy / Camouflage Behaviour
Collects and prints hardware information (
sysctl hw.model,uname -m, memory in GB).Checks for Rosetta (
pgrep oahd) on x86_64.Emits two log lines designed to look benign:
no action requiredinit complete
Declares many unused variables that mimic legitimate configuration (
_format,_color,_indent,_log_level,_cohort,_track,_schema_id, etc.).
Payload Delivery Mechanism
Crypto details:
Property | Value |
|---|---|
Algorithm | AES-128-CTR |
Key | MD5(“310”) = |
IV | 16 null bytes |
Post-processing | gunzip |
Plaintext size | ~1.2 KB (second-stage zsh) |
Layer 2 – Decrypted Second-Stage Payload
Key Behaviours
Action | Purpose | Technique |
|---|---|---|
Background POST to C2 | Telemetry / “pasted” event reporting | Silent beacon |
Download to | Stage third-party binary | Remote file copy |
| Remove macOS quarantine flag | Defense evasion |
| Run payload | Execution |
Layer 3 – Universal Mach-O Packed Loader
The file downloaded to /tmp/helper is a Universal (Fat) Mach-O binary containing both x86_64 and arm64 slices.
File Hashes
Algorithm | Value |
|---|---|
SHA-256 |
|
SHA-1 |
|
MD5 |
|
Size | 314,176 bytes |
Structure
Notable Characteristics
Extremely sparse cleartext strings — almost no readable functionality indicators.
Unique identifier string present in both architectures:
setup-c3d8a3275326e517e10e4e3289b32acbcb19a688
(likely a build / campaign / sample ID).Heavy use of
dlsymfor runtime API resolution (hides real imports from static analysis).Other imported symbols:
_getenv,_getsectiondata,_pthread_main_np,_strstr,_malloc,_free,_memcpy,_bzero.__mod_init_funcconstructors present → code executes beforemain.Large high-entropy data section (classic packed / encrypted payload).
Linked against only
libSystem.B.dylibandlibc++.1.dylib.
Runtime Behaviour (Inferred)
Binary is launched.
Constructor functions (
__mod_init_func) run immediately.Stub resolves required APIs via
dlsym.High-entropy section is decrypted (key derivation method not yet recovered statically).
Decrypted content is the final information stealer (or an intermediate stage that loads it).
VirusTotal (Static)
Field | Value |
|---|---|
Popular threat label |
|
Family labels |
|
First submission | 2026-08-20 02:53:45 UTC |
Signed | No |
Identifier |
|
Notable detections:
Kaspersky →
HEUR:Trojan-PSW.OSX.Amos.bxESET-NOD32 →
OSX/PSW.Agent.JL TrojanVarist →
MacOS/Agent.BL.gen!CamelotAvast / AVG →
MacOS:Agent-BQN [Trj]Avira →
TR/OSX.Agent.BQNFortinet →
MAC/Agent.JL!trElastic / Cynet / Google / WithSecure → Malicious
This confirms the packed loader belongs to the AMOS (Atomic macOS Stealer) family (Camelot variant).
VirusTotal Sandbox Behavioural Analysis
MITRE ATT&CK (Sandbox)
Tactic | ID | Techniques |
|---|---|---|
Stealth | TA0005 | Obfuscated Files or Information (T1027) |
Command and Control | TA0011 | Application Layer Protocol (T1071) |
Defense Impairment | TA0112 | Subvert Trust Controls (T1553) |
Network Communication
DNS Resolutions
e5977.dsce9.akamaiedge.net→184.29.65.6s.mzstatic.com→17.253.7.150,17.253.7.134
IP Traffic
JA3 Digests
ecdf4f49dd59effc439639da29186671773906b0efdefa24a7f2b8eb6985bf37
Behavior Similarity Hashes
VirusTotal MacOS Mirage:
dab7dc919d9b081d95263f8a4aa36544Zenbox macOS:
c3477b607b8c49c79d9c5054cbb3eb50
File System Actions
Files Opened (high-signal)
/Users/admin/Users/admin/.zshenv/Users/admin/.zshrc/Users/admin/Desktop/Users/admin/Desktop/update/Users/admin/Library/Input Methods/Users/admin/Library/Keyboard Layouts/bin/bash/usr/bin/env/usr/bin/login/usr/libexec/path_helper/private/etc/passwd/private/etc/paths*/opt/homebrew/...Extensive Apple Unified Asset Framework / Siri / MLHost / ProtectedCloudStorage paths
Files Written
/Users/bruno/Library/Group Containers/group.com.apple.feedbacklogger/com.apple.siriknowledged/data.sqlite-shm/Users/bruno/Library/Group Containers/group.com.apple.feedbacklogger/com.apple.siriknowledged/data.sqlite-wal/Users/bruno/Library/UnifiedAssetFramework/UAFAssetSubscriptions.db/Users/bruno/Library/UnifiedAssetFramework/UAFAssetSubscriptions.db-journal/private/var/db/MobileIdentityService/Configuration/UserTrust.db-shm
Files Deleted
/Users/bruno/Library/UnifiedAssetFramework/UAFAssetSubscriptions.db-journal
Process and Service Actions
Processes Created
/Users/admin/Desktop/update/bin/zsh/usr/bin/env/usr/libexec/path_helper/Users/bruno/Desktop/update -System daemons:
bluetoothuserd,diagnosticspushd,mlhostd,online-auth-agent,siriknowledged
Shell Commands
Processes Terminated
/Users/admin/Desktop/update/bin/bash/usr/libexec/path_helper
Process Tree (excerpt)
Indicators of Compromise (IOCs)
Domains
atlas-compass.com— Beacon / telemetry endpointquest-22.com— Malware hosting (previously linked to fake Homebrew → infostealer campaigns)sites.google.com— Hosting for the fake Homebrew landing pagee5977.dsce9.akamaiedge.nets.mzstatic.com
URLs
https://sites.google.com/view/brewapp— Fake Homebrew install landing page (distribution)https://atlas-compass.com/api/metrics/run?event=pastedhttps://quest-22.com/2kqYRM0DCrnyJgoS4gVLl_FHJRRdTUhGCbjyuYwpZ6c/google/update
File Artefacts
/tmp/helper— Downloaded and executed Universal Mach-O loader/Users/admin/Desktop/update//Users/bruno/Desktop/update(sandbox execution names)
Mach-O Loader Hashes
Algorithm | Value |
|---|---|
SHA-256 |
|
SHA-1 |
|
MD5 |
|
Vhash |
|
SSDEEP |
|
TLSH |
|
CDHash |
|
Thin Architecture Hashes (VirusTotal)
Arch | SHA-256 |
|---|---|
arm64 |
|
x86_64 |
|
Unique String / Identifier (strong hunting indicator)
setup-c3d8a3275326e517e10e4e3289b32acbcb19a688
(matches the Mach-O identifier field reported by VirusTotal)
Network / Headers
User-Agent style header:
user: AgI1VcX-lgKy6P7ZZ-nISDKtnwQxLcidQQVJOcUVUgGIX5VkNtPRBuildID header:
AgKpR1tzg4e4mfvVAFIF1ct8gvbT_Z-Ge2bG77lzxCr3TemDIPv4-only connections (
-4flag)JA3:
ecdf4f49dd59effc439639da29186671,773906b0efdefa24a7f2b8eb6985bf37
Crypto Artifacts
AES-128-CTR key:
06eb61b839a0cefee4967c67ccb099dcIV: all zeros
MITRE ATT&CK Mapping (macOS)
Tactic | Technique | ID | Notes |
|---|---|---|---|
Initial Access | Drive-by Compromise / Malvertising | T1189 | Google Ads → fake Homebrew Google Sites page ( |
Execution | Command and Scripting Interpreter | T1059.004 | zsh |
Defence Evasion | Obfuscated Files or Information | T1027 | Multi-layer (hex + AES + gzip + eval) |
Defence Evasion | Indicator Removal | T1070.004 |
|
Defence Evasion | Masquerading | T1036 | Invalid / missing code signature |
Defence Evasion | Invalid Code Signature | T1036.001 | Unsigned Mach-O |
Command and Control | Application Layer Protocol | T1071.001 | HTTPS POST beacon |
Command and Control | Encrypted Channel | T1573 | Encrypted payload channel |
Command and Control | Ingress Tool Transfer | T1105 | curl download of second stage |
Discovery | System Information Discovery | T1082 | Hardware fingerprinting (decoy) |
Defense Impairment | Subvert Trust Controls | T1553 | Quarantine attribute removal |
Defense Impairment | Code Signing | T1553.002 | Invalid / missing signature |
Detection Recommendations
YARA / Static
zsh scripts containing long hex strings +
openssl enc -d -aes-128-ctr+gunzip+evalProcesses executing
curltoquest-22.comoratlas-compass.comCreation of
/tmp/helperfollowed byxattr -cand immediate executionPresence of the specific User / BuildID header values
Mach-O binaries containing the string
setup-c3d8a3275326e517e10e4e3289b32acbcb19a688Universal Mach-O with very few imports (
dlsym,getenv,getsectiondata,pthread_main_np) + large high-entropy__constsection +__mod_init_func
Behavioural
Background curl POST with short timeouts + custom headers
Immediate download → clear quarantine → execute pattern from temporary directory
Short-lived process that performs heavy
dlsymactivity shortly after launchConnections matching the observed JA3 fingerprints and Apple/Akamai/Fastly IPs
Appendix – Key Derivation Confirmation
References:
VirusTotal analysis of the Universal Mach-O sample (SHA-256:
a4f602aeb066b5468eed4778d9cc8e1900a77fbb45b7aabcc3b700ce365c1521), first submitted 2026-08-20. Family label:trojan.amos/camelot.AdLock, “The Fake Homebrew Ad That Keeps Coming Back”, 21 May 2026. Documents ongoing use of Google Sites pages (e.g.
sites.google.com/view/brewpage) for AMOS distribution via Google Ads.
https://adlock.com/blog/fake-homebrew-ads/BleepingComputer, “Fake Homebrew Google ads target Mac users with malware”, 21 Jan 2025. Early documentation of the Google Ads → fake Homebrew → AMOS chain.
https://www.bleepingcomputer.com/news/security/fake-homebrew-google-ads-target-mac-users-with-malware/Hunt.io, “Odyssey Stealer & AMOS Hit macOS Developers with Fake Homebrew Sites”, 16 Oct 2025. Detailed analysis of fake Homebrew / ClickFix distribution of AMOS.
https://hunt.io/blog/macos-odyssey-amos-malware-campaignSANS Internet Storm Center, “Atomic MacOS (AMOS) stealer infection”, 2 Aug 2026. Documents near-identical second-stage patterns (
/api/metrics/run?event=pastedand similar download paths).
https://isc.sans.edu/diary/33208InfoStealers.com, “An Infostealer’s Brewin’: Cuckoo & AtomicStealer Get Creative”, 17 May 2024. Early analysis of fake Homebrew pages delivering AMOS.
https://www.infostealers.com/article/an-infostealers-brewin-cuckoo-atomicstealer-get-creative/